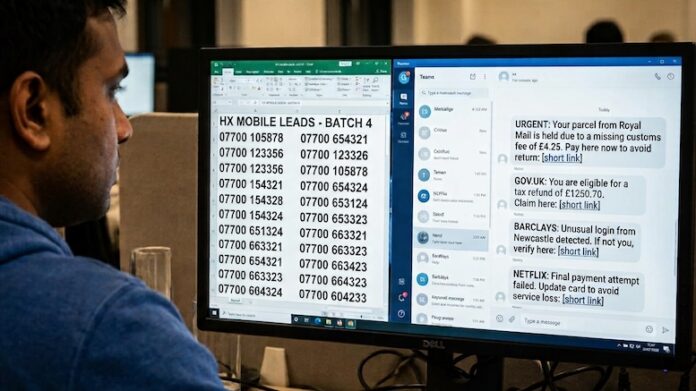
The UK telecoms regulator, Ofcom, announced last week the launch of two separate investigations into telcos suspected of allowing the misuse of UK phone numbers by scammers. The telcos being investigated are:
- Voxbone SA. Voxbone is a cloud communications provider founded in Belgium in 2005. It was acquired by American giant Bandwidth in 2020 for an enterprise value of USD519mn, paid for with a mixture of cash and stock. Voxbone now uses the Bandwidth brand and infrastructure.
- Vonage Business Limited. This cloud communications provider was first incorporated in the UK in 1998 but changed its name after it was acquired by US firm Vonage in 2018 for USD350mn in cash. It was sold by Vonage to Swedish network colossus Ericsson in 2022 for USD6.2bn.
Ofcom is responsible for the allocation of UK phone numbers, and hence has rules about how those numbers can be used. The implication is that Voxbone and Vonage Business Limited assigned UK phone numbers to entities run by scammers. In their statement, Ofcom highlighted concerns about the quality of know-your-customer (KYC) checks applied to the businesses that obtained the services of Voxbone and Vonage Business Limited.
In line with Ofcom’s number rules to protect consumers and industry guidance, phone companies must take appropriate steps to ensure numbers we have allocated to them are not misused by businesses or individuals they have transferred them to. Misuse of numbers could, for example, include using them to facilitate scam calls and texts. Companies must also take steps to ensure that numbers are being used correctly in accordance with the National Telephone Numbering Plan.
In order for phone companies to tackle misuse of numbers, we expect them, among other things, to carry out ‘know your customer’ due diligence checks on their business customers to prevent scammers from accessing valid numbers in the first place. Additionally, they should keep the level of risk posed by a business customer under review by monitoring for potential number misuse and respond proactively to any incidents of misuse that are reported to them.
We have gathered information which has raised concerns about the use of numbers allocated to Vonage Business Limited and Voxbone SA.
Cloud comms is big business, as proven by the valuations of these entities when they were bought and sold by some of the biggest companies in the telecoms sector. Both of these firms have a history which involves rapid growth while they were owned by vulture capitalists. It should come as no surprise that this introduces considerable risk to the general public. Businesses do not grow rapidly by aggressively turning away customers. However, it is impossible to have robust KYC without being prepared to turn away a lot of customers who are willing to pay handsomely for comms services that will be used to scam the public. Buying access to potential victims at scale via a cloud communications provider is cheaper and easier than investing in banks of simboxes — as criminals have begun to do in the USA — or the even more expensive route of driving SMS blasters around, as now occurs in so many other countries.