The UK telecoms regulator, Ofcom, announced last week the launch of two separate investigations into telcos suspected of allowing the misuse of UK phone numbers by scammers. The telcos being investigated are:
- Voxbone SA. Voxbone is a cloud communications provider founded in Belgium in 2005. It was acquired by American giant Bandwidth in 2020 for an enterprise value of USD519mn, paid for with a mixture of cash and stock. Voxbone now uses the Bandwidth brand and infrastructure.
- Vonage Business Limited. This cloud communications provider was first incorporated in the UK in 1998 but changed its name after it was acquired by US firm Vonage in 2018 for USD350mn in cash. It was sold by Vonage to Swedish network colossus Ericsson in 2022 for USD6.2bn.
Ofcom is responsible for the allocation of UK phone numbers, and hence has rules about how those numbers can be used. The implication is that Voxbone and Vonage Business Limited assigned UK phone numbers to entities run by scammers. In their statement, Ofcom highlighted concerns about the quality of know-your-customer (KYC) checks applied to the businesses that obtained the services of Voxbone and Vonage Business Limited.
In line with Ofcom’s number rules to protect consumers and industry guidance, phone companies must take appropriate steps to ensure numbers we have allocated to them are not misused by businesses or individuals they have transferred them to. Misuse of numbers could, for example, include using them to facilitate scam calls and texts. Companies must also take steps to ensure that numbers are being used correctly in accordance with the National Telephone Numbering Plan.
In order for phone companies to tackle misuse of numbers, we expect them, among other things, to carry out ‘know your customer’ due diligence checks on their business customers to prevent scammers from accessing valid numbers in the first place. Additionally, they should keep the level of risk posed by a business customer under review by monitoring for potential number misuse and respond proactively to any incidents of misuse that are reported to them.
We have gathered information which has raised concerns about the use of numbers allocated to Vonage Business Limited and Voxbone SA.
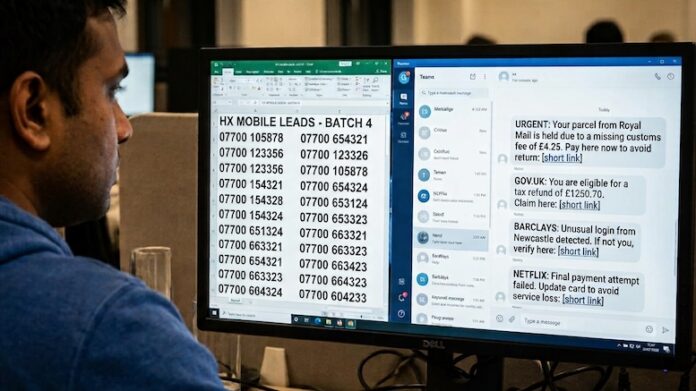
Cloud comms is big business, as proven by the valuations of these entities when they were bought and sold by some of the biggest companies in the telecoms sector. Both of these firms have a history which involves rapid growth while they were owned by vulture capitalists. It should come as no surprise that this introduces considerable risk to the general public. Businesses do not grow rapidly by aggressively turning away customers. However, it is impossible to have robust KYC without being prepared to turn away a lot of customers who are willing to pay handsomely for comms services that will be used to scam the public. Buying access to potential victims at scale via a cloud communications provider is cheaper and easier than investing in banks of simboxes — as criminals have begun to do in the USA — or the even more expensive route of driving SMS blasters around, as now occurs in so many other countries.
Telephony has been infected by the fast and loose culture that generated trillions in wealth for internet and social media companies by turning a blind eye to crime. Telephony providers embrace the internet as a technology because it reduces their costs. However, it also opens the door to a rotten culture that prioritizes profit over protecting the public from crime. Cloud communications providers are the primary vector for this disease. The limp failure of national regulators to toughen their KYC enforcement has allowed telephony to be turned into a wild playground for criminals, just like the rest of the internet. And because of the wealth being generated, the businesses that profit from this regulatory failure have the funds to lobby governments and regulators who barely understand how telecoms work. They will do anything to distract decision-makers from the importance of national authorities enforcing KYC rules in order to prevent criminals gaining access to communication services. Ofcom are to be congratulated for drawing a line in the sand. These investigations show there is at least one regulator who understands that KYC as an essential cornerstone for trustworthy communications.
Like the public, many decision-makers have no comprehension of what a cloud communications provider is, or how their KYC failings lead to the scams that plague everybody’s phones. They only know the names of phone companies with retail brands and have only the vaguest conception of how services sold to businesses can become a threat to the public. So it is telling that telcos with no retail offering have been spending so much on lobbying governments and regulators at both a national and international level. For example, Bandwidth is one of the four companies that has been sending letters to national regulators like Ofcom, telling them to defer to the Cross Border Call Authentication Governance Authority (CBCA-GA) that Bandwidth established with three other American businesses. These people have the cheek to tell national regulators to submit to the decisions of a so-called global authority that was set up without any international consultation, because they supposedly can be trusted to decide which calls can safely be transmitted across borders. They cannot even be trusted to turn away the criminals who knock on their own company’s door.
It is pleasing that Ofcom’s representative has now taken the lead in running GIRAF, the antifraud forum for some national comms regulators that was created as an offshoot of the increasingly flaccid One Consortium initiative. I know Ofcom’s delegate understands the significance of number allocation and assignment to tackling crime when most other people have little comprehension of why they matter. As I observed in my recent report to Europol about the methods to trace calls, you cannot catch a criminal by tracing a call if nobody did proper KYC checks before the call was made.
One Consortium showed their true colors when they rigged the process for circulating their KYC guidance. They threw me out because I blew the whistle on the naked self-interest of an exclusively American group of companies that demanded references to KYC enforcement be removed from the guidance previously published by a supposedly separate association of telcos that they did not belong to. I was given no opportunity to state my version of events. This is important to keep in mind because some of the same people also want to govern telcos through the ‘self-regulating’ regime they are promoting as an alternative to regulators doing the job. Industry shills cannot be trusted to regulate themselves or others. They have neither the instincts, the training, nor the motivation to run a genuine governance regime that will make decisions with billion-dollar consequences for the telcos affected, and for the public that collectively loses billions to the crimes enabled by some of those telcos.
The fundamental problem with every industry association that claims to be collaboratively fighting fraud is the same as the fundamental problem with expecting telcos to self-police KYC. They do not make money by turning away customers. Too many professionals stand on stages only to repeat platitudes about international cooperation to fight crime as if all the bad actors are outside the room. Bad actors are inside the room with us. Bad actors are standing on the stage. But the organizers will throw you out for interrupting or challenging the bad actors because they paid to be on that stage. The unspoken truth is that you cannot be fighting crime if you are cooperating with businesses that enable crime.
A united industry front against scams must be a sham because not every kind of telco has the same interest in fighting scams. The retail mobile operator forced to deal with the tears of the victim of a scam text message is in a very different position to the business that routinely provides wholesale connections to scammers. Pretending there is perfect alignment on how every telco fights crime is a charade unless we have all aligned around the goal of spewing a lot of empty talk whilst never toughening KYC controls or taking any other action that will necessarily reduce the revenues of some telcos. There has been a noticeable trend in the number of people who specialize in empty talk who now stand on stages and offer platitudes about how to reduce crime. 10 years ago, it would have been challenging to find a single person who specializes in public policy or marketing that was willing to publicly express an opinion about how to tackle telecoms fraud. Their default method was to refuse to talk about crime because talking about crime draws attention to crime. Now they dominate the conversation. Sadly, they dominate it through misdirection, which is why they prefer not to speak about the need to enforce consistent and robust KYC rules.
In scenarios like this, other organs of society cannot provide sufficient balance to the greed of unchecked corporations. Journalists cannot do it. The only mass market British newspaper to report the news about Ofcom’s investigation was the Daily Mirror. The BBC did not cover it. None of the broadsheet newspapers covered it. To put this into perspective for readers of Commsrisk from outside of the UK, the Daily Mirror writes news stories in simple language and is not associated with detailed explanations of complicated matters. They did obtain quotes from representatives of Ericsson and Bandwidth. You already know the format for what those companies said: “blah blah… we care a lot… we take it seriously…” and so on. But I do not expect a journalist from the Daily Mirror to be able to challenge empty rhetoric. There are not many telecoms professionals who really understand how weak KYC and the uncontrolled assignment of numbers are enabling crime all over the world. Only a few experts, like Tom Walker in the USA, make the effort to show the scale of fraud being enabled by the supply of phone numbers to criminals. If regulators are not asking serious questions about why so many scammers get access to so many phone numbers, and other industry insiders are punished for highlighting the seriousness of the issue, then we cannot expect some general-purpose journalist to shame us into toughening KYC enforcement.
There is a malign and unforgivable reason for why our industry keeps gassing about technology as a supposed solution to crime. It distracts from the basic requirement — and essential failure — to ask questions about who telcos choose to do business with. Earlier this year, I retired from writing for Commsrisk but all the automated scripts that feed me news from around the world still keep whirling. I find them useful when doing occasional consulting gigs for national and international authorities, such as my report for Europol. Having independent sources of information serves as a useful counterbalance to the fatuous marketing peddled by associations that depend on businesses like Bandwidth for their funding. Building a separate pipeline of news is essential if you want to genuinely understand what is happening. It is exhausting to fight the businesses that prefer disinformation and misdirection to the methods that would genuinely reduce crime. They have been winning the competition for attention, despite the enormous scale of crime enabled by telecoms networks. But I felt this article needed to be written, and not just because it was a glorious opportunity to say ‘I told you so’.
Enforcement of KYC is the topic that bad telcos — and especially bad American telcos — want to avoid talking about. When others remained silent, I preferred to shout, so nobody could pretend they were unaware of how crime occurs. The topic of KYC continues to be shrouded in silence, which is why these investigations by Ofcom are so important, not just in the UK, but for how telcos behave in other countries too. It matters that the UK’s regulator has the courage to take on cloud communication providers, an inherently transnational form of telco, that are subsidiaries of American and Swedish parent companies.
The internet was built on lousy KYC. Social media was built on lousy KYC. Look how societies are now struggling to reverse the consequences of lousy KYC in those arenas. Many of us worry about fake news and disinformation. Scammers are also a source of a certain kind of disinformation. But we will never fix the problem of being told lies if we never check the reputation of the person who is speaking. Trust starts with knowing about the person you are dealing with. Our societies are losing that trust because responsibility has become so diffuse that nobody is ever held accountable for the lies that mislead us. Our communication networks are part of that problem, as is the unbalanced exploitation of those networks by capitalists. It is dangerous to allow businessmen the freedom to make money from networks without forcing them to invest in maintaining the trust that is essential to communication.
Lazily repeating the word ‘trust’ is not enough to restore trust. Actions speak louder than words. KYC should be non-negotiable. Criminals must be turned away. If somebody is negotiating for a lax KYC environment then they serve the needs of the criminal, not the needs of the general public.
You can read Ofcom’s announcement here.