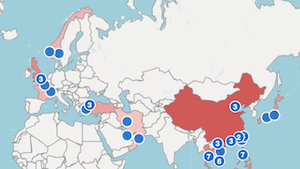
Tismi BV, a telco licensed to operate in eight European countries, has been fined GBP437,500 (USD585,000) by Ofcom, the UK regulator, for “failing to take appropriate and proportionate steps to ensure allocated numbers were not misused, including to perpetrate scams”. Around 366,000 UK phone numbers were sub-allocated by Tismi between November 2022 and January 2025 without adequate due diligence of customers and without adequate monitoring of how those numbers were used in practice. Tismi also lacked formal processes to handle the reports of number misuse they received.
Tismi is headquartered in the Netherlands and is a subsidiary of LINK Mobility, the Norwegian firm which describes itself as the largest Communications Platform as a Service (CPaaS) provider in Europe. LINK Mobility bought Tismi in 2021 through a cash and stock deal that valued their acquisition at EUR20mn (USD22.4mn).
Ofcom’s announcement provided no specific details about Tismi’s failings. The official wording of the regulatory decision concluded with a note saying:
To protect the integrity of other on-going investigations, a non-confidential version of the Confirmation Decision will not be published until a later date.
Commsrisk recently reported on Ofcom’s new investigation into lax know-your-customer (KYC) controls and the potential supply of phone numbers to scammers by cloud comms providers belonging to Bandwidth and Ericsson. This significant fine for Tismi is another indication that the UK’s comms regulator is stepping up the enforcement of number supply rules for those cloud comms businesses which enable scammers. The formal decision about Tismi states:
This penalty is intended to send a clear message to Tismi (and wider industry) that it is not acceptable to effectively allow allocated telephone numbers to be misused and undermine the fundamental purpose of our regulatory rules. It is intended to deter Tismi (and wider industry) from breaching GC B1 and other regulatory obligations in the future and ensure it takes, and continues to take, appropriate steps to ensure compliance from the date rules are effective.
“GC B1” refers to General Condition B1, one of the rules for telcos that are allocated UK telephone numbers. Several clauses of this rule relate to the transfer of phone numbers and are increasingly used to crack down on the supply of phone numbers to criminals. The same rules that Tismi violated were also cited in the new investigations into the subsidiaries of Bandwidth and Ericsson.
Ofcom’s announcement also mentioned another investigation they opened on the same day, into Xtra Phones UK, a small British comms provider that trades as CompareTheNetworks.com. The terms of the investigation into Xtra Phones also cite the same GC B1 rules, plus a different rule related to the spoofing of CLIs. Ironically, the owner of Xtra Phones commented on social media about methods to tackle ‘nuisance numbers’ at approximately the same time as Ofcom publicized their investigation into his business.
The transition from traditional telephony to multinational cloud communications greatly increases the risk of consumer scams unless there is a proportionate tightening of due diligence over who obtains access to networks. The essence of cloud communications is the use of computers to talk to computers in order to instigate more of the calls and messages received by real people. The more computers are involved, and the more they are spread around the world, the harder it is to determine who is responsible for criminal communications. That is why the onus must be on comms providers to question who their customers are and how they use the services they obtain. If telcos do not voluntarily tighten their antifraud controls then the national agencies that are ultimately responsible for the allocation of phone numbers must intervene more often and more forcefully than before.
Any business that genuinely implemented robust KYC would also want robust and consistent enforcement of KYC rules on their competitors to ensure a level playing field. It is telling that industry associations like One Consortium and the Mobile Ecosystem Forum have only delivered token antifraud initiatives without prompting any new investment in KYC controls nor delivering any measurable reduction in criminal activity. Thankfully, it now appears that some regulators are stepping up their enforcement. Because they are dealing with firms that supply comms on a multinational basis, the leading national regulators are changing expectations at an international level.
I was pessimistic about the chances of stopping criminals gaining access to networks after watching American lobbyists battle against any meaningful regulation of the supply of phone numbers in the USA, then succeed in watering down the global KYC guidance issued by One Consortium. The US Federal Communications Commission has the same defect as many telcos — they talk about fighting fraud to distract from their failure to fight fraud. That is to be expected from a regulator that has been so completely captured by the businesses it is supposed to be overseeing. So it is encouraging to see regulators in Europe having the confidence to take the lead in fighting crime. Ofcom has already distinguished themselves with their world-leading policy on tackling the abuse of Global Title, another arena where the Americans prefer talk to action. I believe the mood in Europe is shifting towards a much more vigorous antifraud strategy for comms networks than will be adopted in North America.
The challenge for the Europeans will be to remain steadfast when there is the inevitable Trump-like backlash by American multinationals against European regulation. We have already seen how American corporate interests have joined forces with Trump’s toxic government by seeking to punish Europe for attempting to limit the harms caused by artificial intelligence and social media. The same caustic playbook will be deployed when European regulation demands that American multinational cloud comms providers must hire KYC staff and give them the authority to turn away bad customers. But if Europe cleans up its own telcos first, and shows a measurable reduction in crime as a result, that will make it harder for the Americans to flimflam their way out of the inevitable conclusion: we cannot stop networked crime unless we stop giving criminals access to networks.
Ofcom’s press release about the Tismi fine is here and the official decision is published here.